
By E-commerce 4 Internet Marketers Editorial
FAQ. Connecting a payment gateway, tax or age-gate tool, chargeback helper, KYC vendor, or compliance SaaS to a regulated catalog expands who can read orders, customers, and settlement data. For website owners and developers selling high-risk or regulated products, a weak plugin or abandoned app is not only a malware problem. It is also an acquiring, dispute, and privacy exposure. This FAQ walks through security review signals, update cadence, data access scopes, and exit plans when a payment or compliance app goes quiet. Facts are tied to public WooCommerce, WordPress.org, and Shopify developer materials. It is operational guidance, not legal, PCI, or underwriting advice. It does not invent CVSS scores, and it does not label any named third-party plugin or app as unsafe without primary evidence.
Why do high-risk payment stacks need a stricter vetting bar?
High-risk catalogs already face elevated dispute rates, tighter processor underwriting, and more sensitive buyer data (age attestations, restricted shipping destinations, prescription or telehealth context, hemp batch identifiers, and similar fields). Every new extension that can read those records widens the blast radius of a compromise or an abandoned vendor.
Platform docs make the baseline clear even for ordinary stores. WooCommerce security best practices tell operators to install plugins and themes from reputable sources such as the WordPress Plugin Directory and Theme Directory, to review and update them regularly, to remove software that is no longer maintained or that has known security vulnerabilities, and to avoid nulled or pirated packages. WordPress security guidance for developers states that plugins and themes are key points of weakness, and that developers should never trust user input, should sanitize and validate early, and should escape on output.
For regulated sellers, treat those baselines as the floor. A payment or compliance connection that fails marketplace security gates, requests broad customer scopes without a clear job to do, or has no documented uninstall and data-deletion path should not reach production.
What security review signals should operators check on WooCommerce and WordPress?
Start with distribution channel and automated review, then add your own code and vendor diligence.
Marketplace and directory signals
- Prefer listings that have passed a documented security gate. WooCommerce Marketplace submission rules require products to follow security best practices and to pass Quality Insights Toolkit (QIT) tests that include Security, Malware, Activation, API, End-to-end, PHPCompatibility, and Validation. QIT security docs state that Marketplace submissions and updates must pass security scans that use PHPCS WordPress.Security and WordPress.DB rules, SemGrep insecure-pattern checks, dependency audits (`composer audit`, `npm audit`), WPScan known-vulnerability matching, and gitleaks secret detection.
- WordPress.org Detailed Plugin Guidelines state that directory code should be made as secure as possible, that plugins with confirmed security issues are closed until fixed, and that in extreme cases the WordPress Security team may update a plugin for public safety. Guideline 8 blocks plugins from sending executable code via third-party systems outside documented service patterns. Guideline 15 requires version numbers to increment so users are notified of updates.
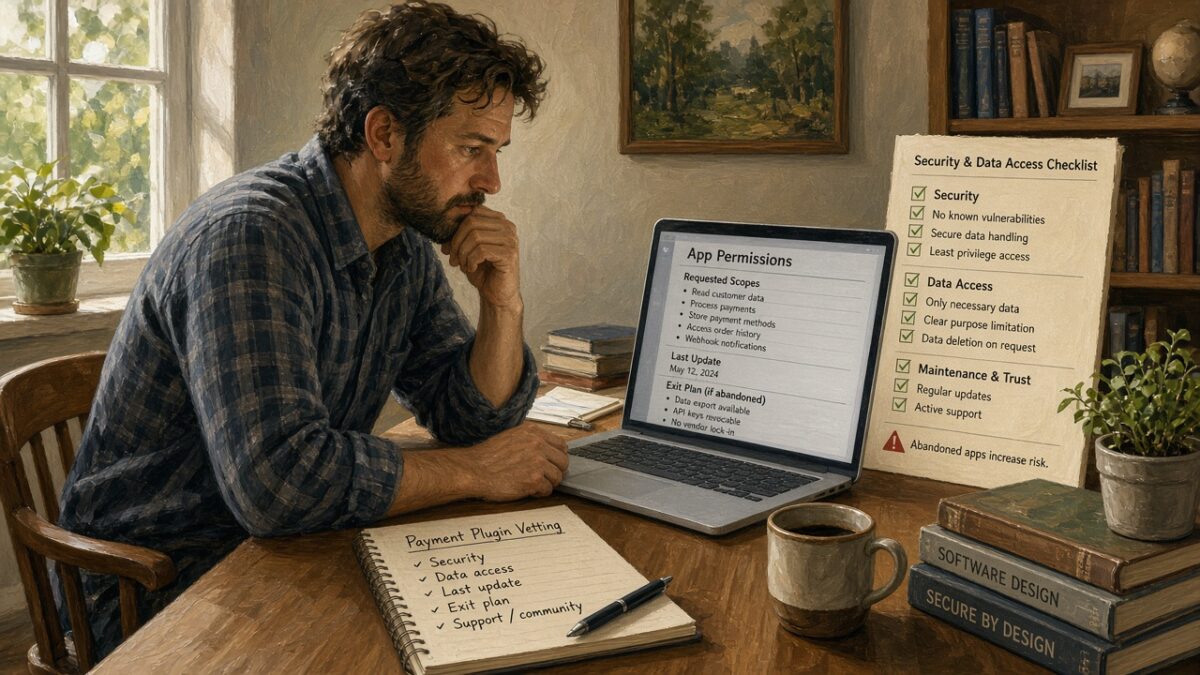
Operator review checklist (before connecting a high-risk gateway or compliance tool)
- Confirm the package comes from WordPress.org, WooCommerce.com, or a vendor you can contract with, not a cracked zip.
- Read the changelog and "last updated" date. Long silence plus a payment or KYC role is a stop signal until you have a replacement plan.
- Open the plugin settings and privacy policy. Map which admin capabilities it needs, which remote hosts it calls, and whether it stores PAN, tokens, government IDs, or age documents off-site.
- Prefer gateways that keep card data in a PCI-scoped iframe, redirect, or hosted field model rather than writing raw card numbers into your WordPress database. (Confirm the exact capture method in the vendor's current docs. Do not assume SAQ outcomes.)
- Stage the install on a clone. Watch for unexpected admin users, outbound callbacks, and new cron jobs before production.
WooCommerce's own security guide also recommends staging tests, strong unique passwords, limited login attempts or 2FA, SSL for data in transit, backups stored off-site, and continuous monitoring. Those controls do not replace plugin vetting. They limit damage when something slips through.
How do Shopify App Store rules constrain payment and compliance apps?
Shopify App Store requirements are explicit about security transport, scope minimization, and payment-app architecture.
Security and scopes. Section 3.1 requires a valid TLS/SSL certificate for data exchanged with the app. Section 3.2 requires apps to request only the access scopes needed to function, and says Shopify may demand proof that requested scopes are necessary. Optional scopes are recommended when not every merchant needs the same data. Shopify's January 24, 2025 changelog states that beginning February 1, 2025, App Store submissions are checked for scopes that need Shopify permission for approved use cases, and that unnecessary or non-approved scopes can be removed.
Payment apps. Category 5.2 requires payment apps to use the Payments Apps API (and mandatory webhooks), to remain standalone rather than embedded admin apps, to offer test mode, to allow buyers to abandon payment and return to checkout, and to avoid upsells inside the payment flow. Payments apps are not permitted to use arbitrary Admin API scopes beyond that payments surface. Requirement 1.1.7 separately states that Payment Gateway apps must be authorized and built with the Payments API.
Protected customer data. Shopify's protected customer data docs define levels of access. Level 1 covers customer data excluding name, address, phone, and email fields. Level 2 adds those identifying fields. Public apps need Partner Dashboard approval, must process only the minimum personal data required, must disclose purposes to merchants, must apply retention limits, and must encrypt data at rest and in transit. Level 2 adds backup encryption, environment separation, access logging, staff access limits, strong staff passwords, and an incident response policy.
Compliance webhooks. Public App Store apps must implement `customers/data_request`, `customers/redact`, and `shop/redact`. Shopify's privacy compliance docs state that apps must verify HMAC signatures (return 401 on invalid HMAC), acknowledge with a 2xx response, and complete the action within 30 days unless legally required to retain data. After uninstall, Shopify sends `shop/redact` 48 hours later so the app can erase that shop's stored data.
Merchant takeaway: an App Store listing is necessary but not sufficient. Open the install consent screen and write down every scope. If a tax, fraud, or analytics app asks for `write_orders`, `read_all_orders`, or identifying customer fields without a documented need, pause and demand a written data map.
Which data access scopes deserve the closest scrutiny?
Treat scopes as production entitlements, not marketing bullets.
On Shopify, the access scopes reference explains that write permission includes read, that apps should request only what they need, and that some scopes require Shopify approval before they can be declared. High-sensitivity examples for payment and compliance stacks include:
- `read_orders` / `write_orders` (orders from the last 60 days by default)
- `read_all_orders` (orders beyond the default window, Partner Dashboard approval required, and App Store rule 3.2.1 says the app must demonstrate need)
- `read_customers` / `write_customers`
- `read_customer_payment_methods`, `read_own_subscription_contracts`, `write_own_subscription_contracts` (subscription and vault-adjacent, approval required)
- `write_payment_sessions` / payments-app scopes
- Protected customer fields (name, address, email, phone) under the separate protected-customer-data review
Shopify Help on apps and personal information likewise notes that order apps may request recent orders (about 60 days) or all orders, and that Shopify reviews all-orders access for necessity.
On WooCommerce / WordPress, there is no single OAuth scope screen comparable to Shopify's install prompt. Capability checks, REST API keys, webhook secrets, and "connect to vendor" OAuth apps substitute. Ask:
- Does the plugin create custom roles or grant `manage_woocommerce` broadly?
- Does it store API keys in `wp_options` in plaintext?
- Does it export full order CSV or PII to a vendor URL on every checkout?
- Can you rotate keys without a support ticket?
If the vendor cannot answer those questions in writing, do not connect the live MID.
What update cadence and maintenance signals should operators require?
Neither WooCommerce nor Shopify publishes a universal "must ship every N days" rule for every third-party tool. Operators still need a maintenance bar before wiring the tool into settlement.
Verified signals you can require in a vendor contract or runbook:
- Compatible with current platform majors. Woo Marketplace submission rules require support for the two latest major releases of WooCommerce and WordPress. Treat that as the minimum bar for any payment plugin you keep.
- Security patches ship as version bumps. WordPress.org guideline 15 exists so users get update notices. A silent security fix with no version change is a process failure.
- Marketplace security re-checks on updates. QIT docs state new submissions and updates must pass security tests. Prefer vendors who show recent Marketplace or directory releases rather than a one-time zip from 2019.
- Documented support channel and status page. Abandoned forums plus bounced security mail is an exit trigger.
- Dependency hygiene. QIT flags vulnerable Composer and npm packages. Ask vendors how they monitor `composer audit` / `npm audit` results for payment SDKs.
WooCommerce security best practices separately urge enabling automatic updates for WordPress core where appropriate and regularly installing WooCommerce and plugin updates because updates often include security patches. For high-risk stacks, schedule a monthly review of every extension that can touch checkout, subscriptions, tax, fraud, or identity documents. Remove anything idle.
What exit plan should exist if a payment or compliance app is abandoned?
Assume every vendor can disappear. Build the off-ramp before go-live.
Technical exit
- Keep gateway credentials, webhook signing secrets, and reconciliation exports under your control, not only inside the plugin UI.
- Prefer architectures where tokens live at the processor (customer vault / CIM / network tokens) so uninstalling a middleware plugin does not destroy chargeable payment methods.
- Document the uninstall order: disable webhooks, rotate keys, uninstall, confirm no leftover mu-plugins or must-use drop-ins, purge vendor cron, and re-test checkout on staging then production.
- On Shopify, uninstall triggers the 48-hour `shop/redact` path for App Store apps. Still export your own order and dispute evidence first. Do not rely on the vendor to keep your chargeback files.
Vendor and directory exit
- WordPress.org documents a formal take over an existing plugin process when developers go silent, including contacting the original author, submitting reviewed code, and a waiting period before transfer. That process can restore maintenance for directory plugins, but it is not instantaneous and is not guaranteed. Closed-for-security plugins must have issues fixed before adoption. Do not bet a live high-risk MID on a future adoption request.
- If the tool is commercial SaaS, require contract language for data export formats, deletion timelines, escrow or source-access on insolvency (when negotiable), and a migration window that covers monthly close and representment cycles.
Business continuity tests
Quarterly, run a tabletop: "Vendor X stops answering." Name the replacement gateway plugin or app, the person who rotates keys, the estimated hours to cut over, and which disputes or tax filings would stall. If you cannot name a replacement, you are not ready to connect.
What is a practical pre-connect checklist for a high-risk stack?
Use this sequence before any production OAuth install or plugin activation that can see payments or regulated order data.
- Business fit. Confirm the tool is allowed for your MCC / vertical with your acquirer or ISO in writing.
- Distribution. WordPress.org, WooCommerce Marketplace, Shopify App Store, or a contracted enterprise vendor only.
- Security gate. Evidence of QIT security pass, App Store approval, or an independent review you commissioned. No invented scores. If you lack primary evidence, say "unverified" and keep the tool off production.
- Scope map. List every Shopify scope or WordPress capability and matching data field. Reject unused write scopes.
- Protected data. If customer name, address, email, phone, government ID, or health-adjacent data leaves your store, require encryption, retention limits, and a signed data processing exhibit.
- Update SLA. Written expectation for critical security fixes and platform major-version support.
- Logging. Admin audit log of configuration changes and outbound API calls.
- Backup and staging. Restorable backup taken immediately before install. Staging dry run completed.
- Exit kit. Key rotation steps, replacement product shortlist, export job, and uninstall runbook tested once.
- Owner. A named engineer or agency retains the runbook. "The freelancer who installed it" is not an owner.
Bottom line for regulated ecommerce teams
Plugin and app vetting is part of payment operations, not a one-time IT chore. WooCommerce and WordPress publish clear maintenance and secure-coding expectations. Shopify publishes scope minimization, protected customer data levels, payment-app constraints, and mandatory redaction webhooks. Use those primary rules to decide what may touch a high-risk checkout. Skip rumor-based "unsafe plugin" lists that lack primary citations, skip invented vulnerability scores, and keep an exit plan that survives vendor silence.
Sources
- WooCommerce security best practices
- WooCommerce Marketplace submitting your product
- QIT security tests
- WordPress security (developer handbook)
- WordPress.org Detailed Plugin Guidelines
- Take over an existing plugin (WordPress.org)
- Shopify App Store requirements
- Shopify API access scopes
- Work with protected customer data (Shopify)